Choosing the right supplier can determine whether a security system protects your premises or simply creates expensive noise. The process begins with a clear assessment of your site, risks, staff routines, and future expansion plans. A small warehouse may need reliable cameras, controlled entry, and tested alarms. A multi-site business may require centralized monitoring, cloud access, and consistent maintenance.
The key question is “how to choose a reliable security system supplier” without trusting polished promises alone. Examine the supplier’s experience with properties similar to yours. Request verifiable project references, product certifications, response-time commitments, and detailed warranty terms. Ask who will install the equipment, who receives alerts, and how faults are handled at 2 a.m. A dependable supplier should explain these details plainly. Vague answers matter.
Bruce Schneier, a respected security technologist and author, once said, “Security is a process, not a product.” That principle should guide every supplier evaluation. Good equipment cannot compensate for poor installation, neglected updates, weak user training, or missing maintenance records. Visit a completed installation if possible. Look closely at cable routing, camera angles, access points, and the clarity of control-panel instructions. These physical details reveal more than a sales presentation.
There is no perfect choice. A supplier may have strong technology but limited local support. Another may offer excellent service but fewer integration options. I would compare both before signing anything. A reliable partner welcomes difficult questions, documents its promises, and helps you measure performance after installation. That ongoing accountability is often the difference between security that looks impressive and security that works.
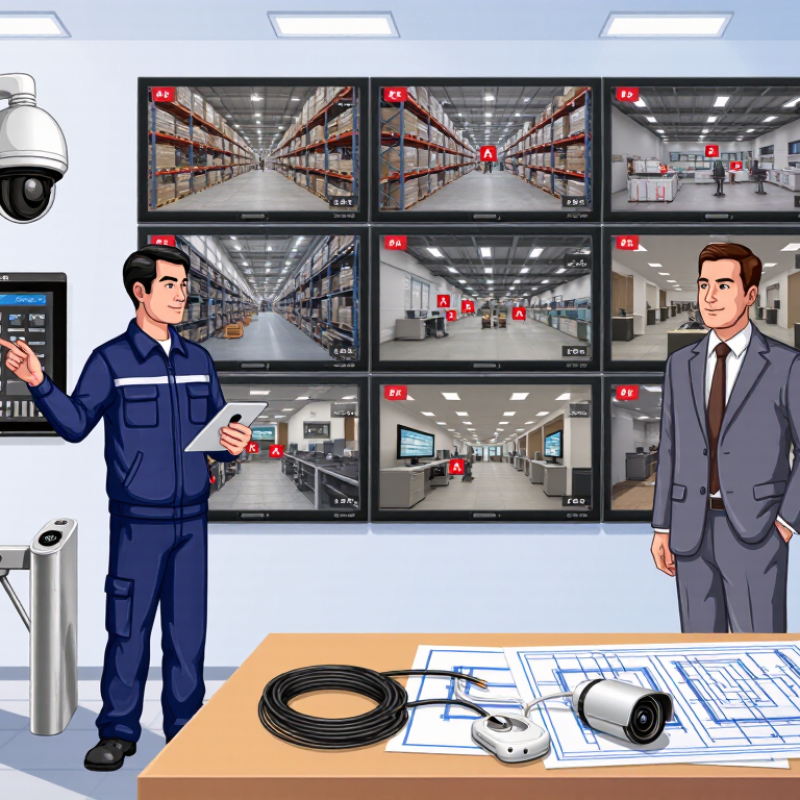
Choosing a security system supplier should begin with control coverage, not attractive hardware. Map each requirement to NIST CSF 2.0 and ISO/IEC 27001:2022. NIST’s six functions— Govern, Identify, Protect, Detect, Respond, and Recover— turn a sales conversation into a testable security plan. ISO/IEC 27001 adds a risk-based management system and 93 Annex A controls. Ask suppliers to show evidence for each relevant control. Claims are not evidence.
The 2024 Data Breach Investigations Report found the human element in 68% of breaches. That figure makes identity controls, access reviews, training, and phishing-resistant authentication practical selection criteria. Under Govern, request named owners, escalation paths, supplier-risk reviews, and audit rights. Under Detect and Respond, inspect alert samples, retention periods, response targets, and forensic export procedures. A credible supplier should explain how one access anomaly becomes an incident record.
Request a control matrix, independent assessment reports, penetration-test summaries, and corrective-action dates. Verify contract language for logging, data location, subcontractors, vulnerability disclosure, and secure deletion.
The Cost of a Data Breach Report 2024 placed the global average breach cost at 4.88 million dollars. That number is a warning, not a procurement formula.
I would still test the system during a power loss and a false alarm. Real sites are messy. One weakness remains: mappings can look complete while ownership is unclear. Require live demonstrations, measurable service levels, and quarterly control reviews before approval.
Choosing a reliable security system supplier starts with standards, not glossy demonstrations. MarketsandMarkets estimated the video surveillance market at about USD 53.7 billion in 2024, with strong growth expected through 2029. This expansion increases supplier choice, but also increases verification risk.
For video surveillance, request evidence against IEC 62676. Check image quality, recording performance, environmental testing, and system interoperability. For intrusion and hold-up alarms, verify EN 50131 compliance. Ask whether the certificate covers the exact detector, control panel, communication path, and security grade. For access control, review UL 294 documentation. Confirm that the tested configuration matches the doors, readers, power supplies, and software you will deploy.
Certificates are not enough. A 2024 access control market report from Fortune Business Insights valued the sector at more than USD 10 billion, showing why certification claims deserve careful review. Ask for current test reports, certificate numbers, issuing laboratories, and production-site traceability. Check firmware revision details too. A small revision can change tested performance. Suppliers should explain maintenance intervals, cybersecurity updates, replacement parts, and failure behavior in plain language. In a sample audit, compare the certificate model number with the quotation and delivered unit. This step is often missed. It should not be. A supplier that avoids precise answers may still offer attractive pricing, but the operational risk remains difficult to measure.
Top Tips to Choose a Reliable Security System Supplier
The 2024 Data Breach Investigations Report found that 68% of breaches involved a non-malicious human element. Employees clicked unsafe links, reused passwords, or misdirected sensitive information. A reliable security system supplier should address these everyday weaknesses, not only install cameras and alarms.
Ask suppliers how their systems protect user accounts, remote access, and stored footage. Request evidence of multi-factor authentication, encryption, software updates, and independent security testing. During supplier interviews, I prefer specific answers over polished promises. Can they explain their response process after a compromised account? Can they show update records and access logs? If not, pause.
Tips: Request a written incident-response plan. Check whether each administrator receives a separate account. Confirm that former staff lose access immediately. Ask how long logs remain available. Small details matter.
The report also highlights social engineering, where people are manipulated into revealing access or approving harmful actions. Suppliers should provide practical training, clear warning prompts, and simple reporting channels. Test these controls with a harmless internal exercise. Results may feel uncomfortable. That is useful.
Do not judge security by product features alone. Examine the supplier’s support team, subcontractors, data handling, and maintenance practices. Ask for references from organizations with similar sites and risks. Verify their claims through contracts, audit documents, and technical demonstrations. One weakness remains: even strong technology depends on tired, rushed people. A dependable supplier should acknowledge that openly and design around it.
| Assessment Dimension | 2024 DBIR Finding | Risk Level | What to Verify in a Supplier | Recommended Evaluation Evidence |
|---|---|---|---|---|
| Human involvement in breaches | Human-related factors were involved in 68% of confirmed breaches, including social engineering and mistakes. | Critical | Confirm that the supplier includes identity protection, security awareness support, strong authentication, and controls that reduce user error. | Security architecture, authentication design, user-role model, training materials, and incident-response procedures. |
| Social engineering exposure | Social engineering remained a significant breach pattern, with attackers frequently targeting people rather than only technical weaknesses. | High | Check whether the system supports phishing-resistant authentication, suspicious-login alerts, approval workflows, and access verification. | Multi-factor authentication options, alert examples, workflow demonstrations, and documented anti-phishing controls. |
| Vulnerability exploitation | Exploitation of vulnerabilities accounted for 14% of breaches and doubled compared with the previous year’s proportion. | High | Assess patch management, vulnerability scanning, secure configuration, software update procedures, and exposure monitoring. | Patch-service-level targets, vulnerability-management policy, penetration-test summaries, and update logs. |
| Third-party involvement | Third-party participation in breaches doubled to 15%, showing that supplier and integration risk must be assessed directly. | High | Review how the supplier manages subcontractors, cloud services, remote support, APIs, data sharing, and privileged access. | Third-party risk policy, data-flow diagram, subcontractor register, access-control records, and contract security clauses. |
| Ransomware resilience | Ransomware appeared in 23% of confirmed breaches, making recovery capability an important supplier-selection criterion. | High | Verify immutable backups, recovery testing, endpoint protection, network segmentation, and a documented ransomware response plan. | Backup test reports, recovery-time objectives, business-continuity plan, segmentation design, and incident-exercise results. |
| Access privilege control | Human behavior can turn legitimate access into a security weakness when permissions are excessive, shared, or poorly reviewed. | High | Require least-privilege access, role-based permissions, privileged-session monitoring, approval controls, and prompt access removal. | Role-permission matrix, access-review schedule, privileged-access logs, joiner-mover-leaver process, and audit reports. |
| Operational error reduction | Human error is included in the 68% human-element breach category, demonstrating the value of preventive automation and safeguards. | Medium | Look for automated validation, confirmation prompts, safe defaults, configuration templates, and change-control mechanisms. | Change-management policy, configuration baseline, approval workflow, rollback process, and error-prevention demonstrations. |
| Incident detection and response | The DBIR findings show that both human actions and technical weaknesses can contribute to breaches, requiring coordinated response capabilities. | High | Evaluate monitoring coverage, alert triage, escalation paths, forensic support, breach notification procedures, and response availability. | Sample incident timeline, monitoring dashboard, escalation matrix, response-service terms, and tabletop-exercise records. |
| Security governance and accountability | The scale of human-element involvement supports a governance approach that measures behavior, access, training, and control effectiveness. | Medium | Confirm that the supplier has named security responsibilities, measurable controls, regular assessments, and transparent reporting. | Security governance chart, control framework mapping, audit results, risk register, and key security performance indicators. |
A reliable security system supplier must support GDPR response, not merely prevent intrusion. Under GDPR Article 33, organisations generally have 72 hours to notify the relevant supervisory authority after discovering a personal data breach. Delayed supplier communication can consume that window quickly. Ask how the system detects unusual access, preserves evidence, and alerts your privacy team.
Tip: Request a written incident process. It should name escalation contacts, response times, logging methods, and support availability. Check whether administrators can restrict exported footage, disable shared accounts, and review every viewing event. Encryption in transit and at rest matters, but poor access control can still expose sensitive recordings.
The Verizon 2024 Data Breach Investigations Report found that the human element appeared in 68% of breaches. That makes role-based access and phishing-resistant authentication practical requirements. IBM’s 2024 Cost of a Data Breach Report placed the global average breach cost at 4.88 million US dollars. A supplier cannot remove every risk, though it should reduce confusion during an incident. Ask for processor terms, retention settings, deletion evidence, and breach-notification commitments that are faster than the legal deadline.
Tip: Test the workflow before purchase. Create a harmless mock alert and measure who receives it, how quickly logs appear, and whether evidence remains readable. I would not trust a polished dashboard alone. Independent penetration-test summaries and clear audit records reveal more. Sometimes the cheapest system creates the most expensive uncertainty.
Choosing a security system supplier requires more than comparing camera counts or installation prices. In project reviews, I look at the support path after handover. Who answers at 2 a.m.? How quickly can an engineer reach the site? Ask for named escalation levels, response windows, and service coverage by location. Test the process with a realistic fault scenario. A polished presentation proves little.
A useful service-level agreement (SLA) should define response, restoration, reporting, and remedies. Check whether “response” means an email or active troubleshooting. Review uptime calculations, exclusions, and planned maintenance rules. Then model lifecycle costs over five to ten years. Include licenses, storage, firmware work, training, replacement parts, energy, and site visits. Cheap hardware can become expensive when proprietary components age. I once underestimated battery replacement and network changes. That mistake changed our evaluation worksheet.
Independent audit evidence adds weight, but only when it is current and relevant. Request the audit scope, testing period, exceptions, corrective actions, and the auditor’s independence statement. Do not accept a certificate without context. Compare findings against your risk profile and operating environment. Ask how access logs are protected, reviewed, and retained. Evidence should connect to daily controls, not sit in a sales folder. If a supplier cannot explain one unresolved finding plainly, pause the decision. Trust needs documentation, and sometimes uncomfortable questions.
This practical scorecard gives the greatest weight to independently verified security controls and transparent five-year lifecycle costs. Suppliers should also provide measurable support commitments and clearly defined service-level agreements with response and restoration targets. The percentages are procurement-model weights, not market-share or company-performance data.
Mapping turns broad promises into testable controls. Use governance, identification, protection, detection, response, and recovery categories. Claims are not evidence. Ask for a control matrix and named owners.
Request independent assessment reports, penetration-test summaries, corrective-action dates, and audit rights. Check certificate numbers and issuing laboratories. Also inspect firmware versions. Paperwork can still hide gaps.
Require role-based permissions, regular access reviews, and phishing-resistant authentication. Shared accounts should be disabled or tightly controlled. Every viewing event should create a readable log. People remain a major weakness.
Review image quality, recording performance, environmental tests, and interoperability evidence. Compare the certified model with the quoted unit. Test footage during network loss. A polished display proves little.
Confirm that certificates cover the exact detector, panel, communication path, reader, power supply, and software. Check the required security grade. Ask how the system behaves during power failure. Small configuration differences matter.
Check encryption during transfer and storage, retention settings, deletion evidence, and export restrictions. Administrators should review every footage access. The system should alert privacy staff quickly after unusual activity.
Create a harmless mock alert. Measure who receives it, when logs appear, and whether evidence stays readable. Review escalation contacts and response targets. Dashboards can look better than reality.
Define logging, data location, subcontractors, vulnerability reporting, secure deletion, and notification duties. Require quarterly control reviews and measurable service levels. I might still miss something. That is why live testing matters.
Choosing the right supplier requires more than comparing product features or prices. This guide explains how to choose a reliable security system supplier by first mapping your organization’s needs to recognized cybersecurity and information security frameworks. It also recommends verifying surveillance, access control, and related products against applicable technical standards, while evaluating whether the supplier follows sound practices for authentication, encryption, updates, access management, and incident response.
The article further highlights the importance of addressing human-related security risks identified in recent breach data, reviewing privacy procedures such as timely breach notification, and examining how personal information is protected throughout the system lifecycle. Buyers should compare technical support, service-level agreements, maintenance coverage, upgrade policies, total lifecycle costs, and independent audit evidence. A dependable supplier should offer transparent documentation, responsive assistance, scalable solutions, and measurable commitments to security, privacy, reliability, and long-term service quality.
SMTR SmartLiving